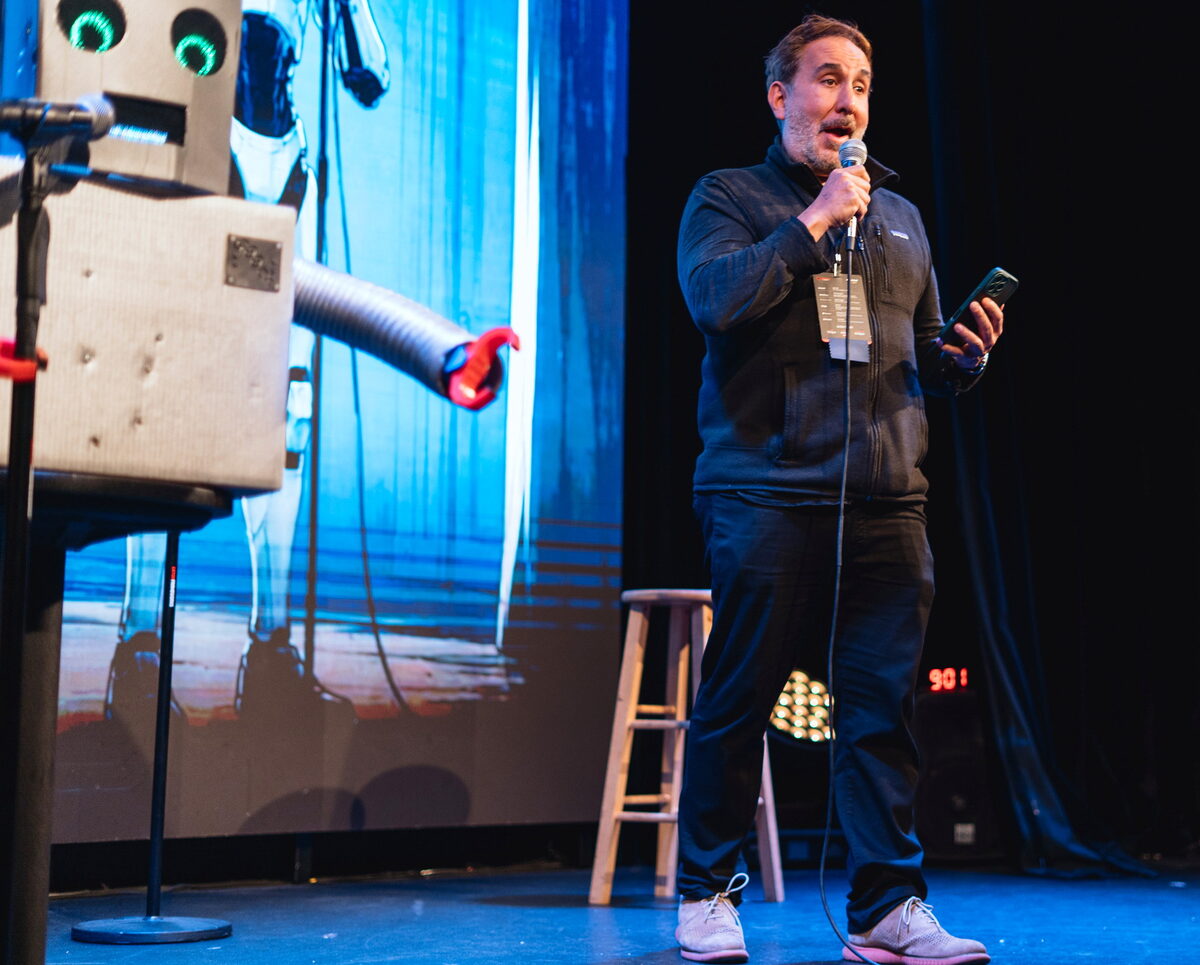
Teams of 300+ across four continents. Cyber strategy, insider threat, regulatory compliance, supply chain risk, and product innovation with top-tier vendors. Creator of ICHI, the Internet Cyber Health Index.
Slow inbox by design — I'll get back to you. Also on Substack.
I lead enterprise-wide cybersecurity and risk programs at global financial institutions and Fortune 100 companies, building and transforming security organizations and leading teams of 300+ across four continents. I sit at the intersection of boards, regulators (SEC, OCC, FRB), and engineering teams, aligning technology strategy with business resilience.
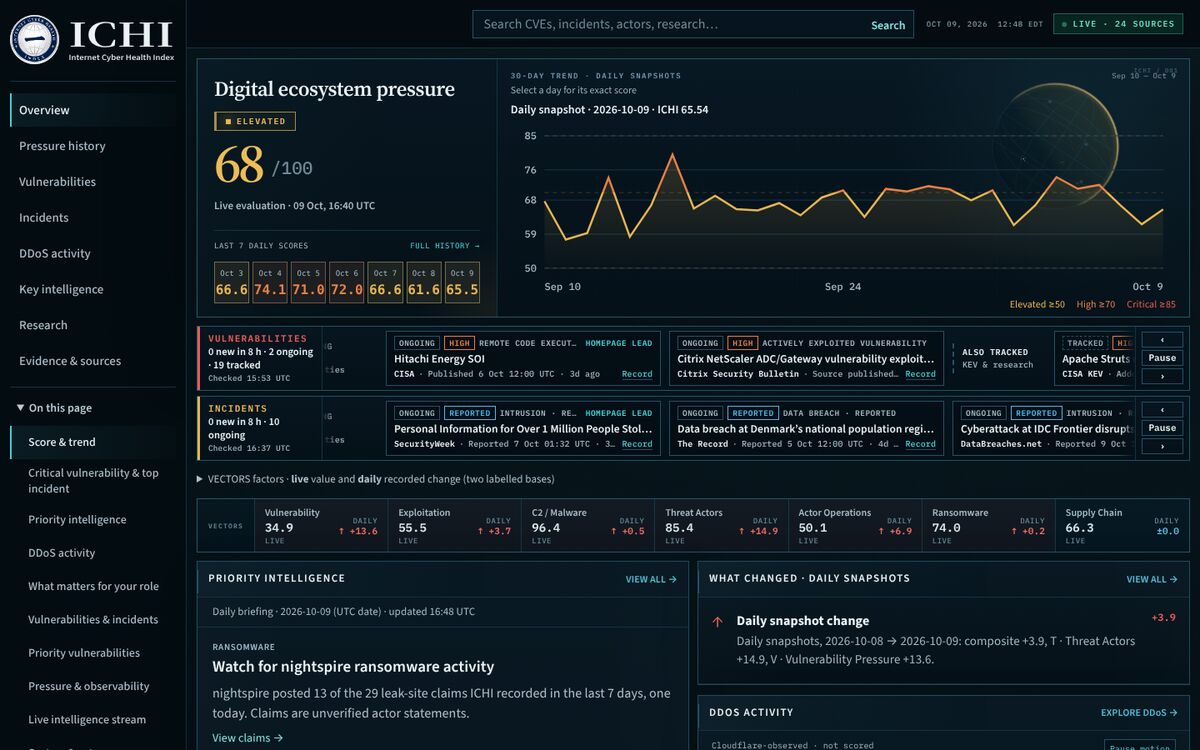
A cyber resilience observatory that tracks the daily condition of the digital ecosystem and distills it into a single, executive-readable score.
+ Select any role for the full record
+ Select any piece for the full abstract and link
An authoritative treatment of the practical security challenges around AI deployment in enterprise environments — governance, threat modeling, and the unique risk surface introduced by ML at scale, drawn from operational experience across global financial institutions. Volume V · Chapter 6 · pp. 113–124.
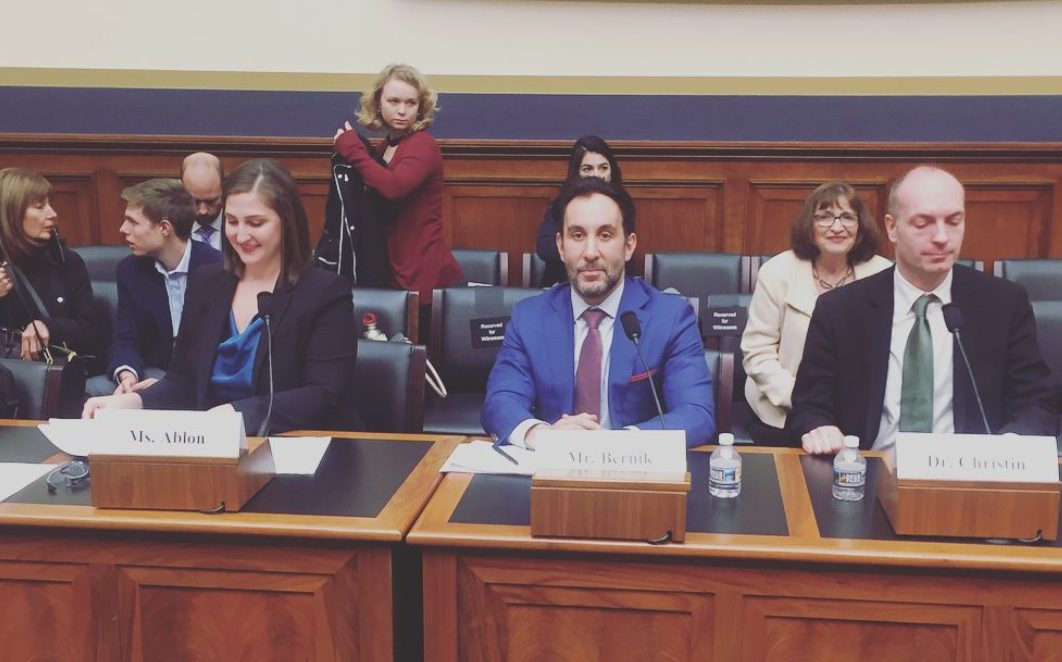
Read at De Gruyter →Public-private cooperation, the inadequacy of the SSN as a digital identity credential, and the case for modernizing federal procurement of next-generation security solutions.
"The financial sector is ready and waiting. As good a job as institutions like Bank of America and US Bank are doing, they can't be expected to deter a nation state on their own." — Statement for the Record · Subcommittee on Financial InstitutionsRead full testimony (PDF) →
Feature on the shifting cybercrime landscape facing banks — fileless malware, cryptojacking, business email compromise and third-party access. As McAfee’s chief strategist for financial services, Joe names the usual suspects — insiders, organized criminals, nation-state actors and fast-moving technology that outpaces the controls needed to protect customers — and warns that “unruly regulations” such as GDPR “cost banks resources” that could go to the fight.
Read the feature →Building trust with business partners, the rise of organized cybercrime targeting financial institutions, and the shift from infrastructure-centric security to business-risk leadership. CISO Profile · Fifth Third Bank.
Read profile → Listen to the interview →Why people are the first and most important line of defense against social engineering and advanced threats. Podcast transcript · BNY Mellon.
Read transcript (PDF) →+ Select any engagement for details and link
Spoke as Bank of America’s Business Information Security Executive for Global Banking & Markets, Enterprise Risk & Finance, alongside CISOs from across finance, infrastructure and industry.
View speaker lineup →Speaker profile covering two decades of cyber leadership as CISO and head of information risk at ABN AMRO, Fifth Third Bank and BNY Mellon, roles with the Federal Reserve Council on Fraud, FS-ISAC and OWASP, and advisory work for the Congressional Banking Committee.
View speaker profile →Featured speaker profile from the International Economic Forum of the Americas, covering a career in global financial cybersecurity and work with FS-ISAC and the Federal Reserve.
The fastest way to reach me is LinkedIn, or email me directly. For writing and ongoing analysis, find me on Substack, and follow the daily read on internet risk at ICHI.global.
Slow inbox by design — I'll get back to you. bernik@gmail.com